How do I migrate Password Policy?
With the retirement of Server 2016, a question that has risen in popularity is how I migrate my password policy to another server to continue using the product without any issues?
The simple answer is not a lot needs to be done since all of the configuration is stored in Group Policy and Active Directory. If you are also in the process of evaluating which software should be installed at this time as well it is recommended only the Password Policy Sentinel be installed on your domain controllers.
Microsoft best practices for securing a domain controller focus on reducing the attack surface, hardening configurations, and isolating the server from general network traffic and the internet.
You would copy over the MSI related to the component you are moving to a different server:
Where are these files located?
Once you download the setup from from In C:\temp\SpecopsPasswordPolicy_Setup_(version number)\Products\SpecopsPasswordPolicy where Password Policy Domain Administration is currently installed.

Password Policy Domain Administration
Recommendations:
- It is suggested to install this on a member server, but can be installed on a domain controller where policies are managed without issue.
- This should be installed in a central location accessible to anyone who administers Specops Password Policy. It does not need to be installed in multiple locations as I can cause issues with outdated versions when new versions of the product become available.
How to Install:
Copy and Install the SpecopsPasswordPolicyAdmin-x64.msi on the new server.
Password Policy Arbiter
Recommendations:
- This component should also only be installed on a member server and not a domain controller.
- Please also do this prior to removing the older arbiter to ensure you have continuity between your breached password protection complete checks.
- There should be multiple arbiters (2 at minimum) for redundancy. It is also important to note that these operate in a round robin capacity and not an active passive capacity.
How to Install:
Copy and Install the SpecopsArbiter-x64.msi on the new server.
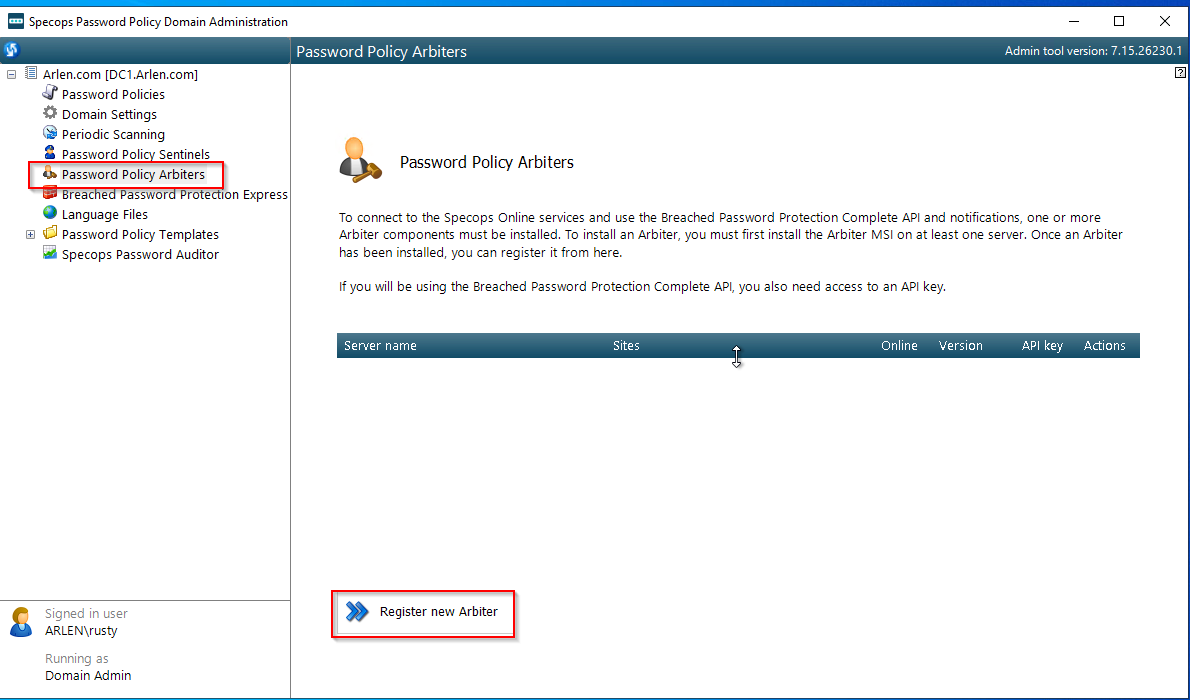
Once that is done, launch Password Policy Domain Administration and navigate to the “Password Policy Arbiters” section and select “Register new Arbiter” and enter the name of the server, you wish to use and check names:
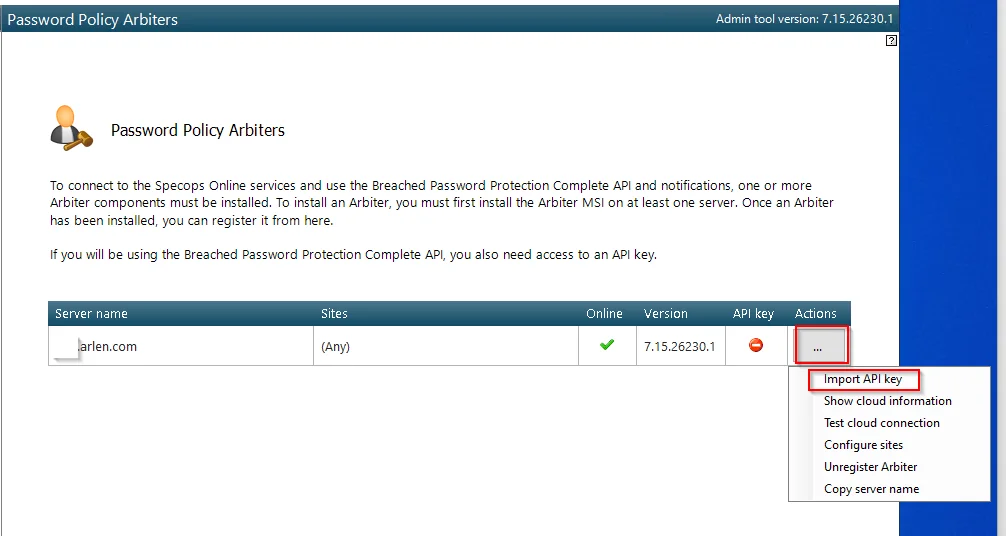
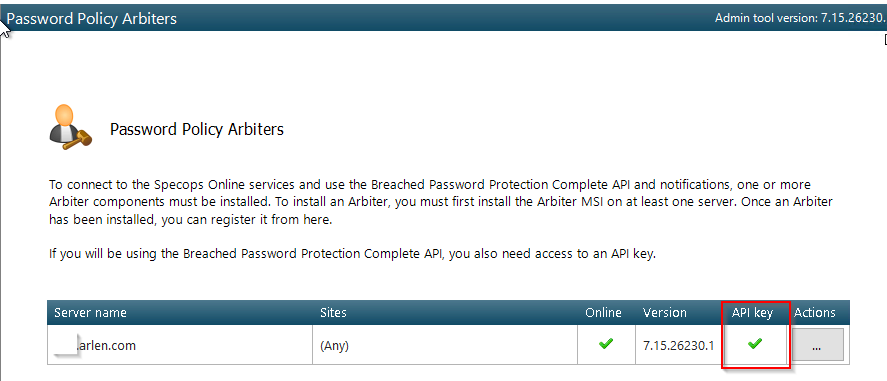
Click Actions>Import API Key. If you do not have an API key, please contact support.
If during this migration have a new Domain Controller:
Copy and Install the SpecopsPasswordPolicySentinel-x64.msi to the new Domain Controller and run the msi and restart the machine to complete the installation.
If you are moving the PDC Emulator role:
Make sure the sentinel is installed on both the current PDC and what will be the new PDC. From there, transfer the role(s) as normal (https://learn.microsoft.com/en-us/troubleshoot/windows-server/active-directory/view-transfer-fsmo-roles). Once the role(s) have been transferred, restart both DCs and verify the PDC and Web API are both showing the correct server. If the Web API is still shown as disabled, you can add/adjust the registry setting in this article and restart the Specops Password Sentinel Service, which should then show the Web API status listed as “OK”. This will also cause a new certificate to be automatically generated on the new PDC.

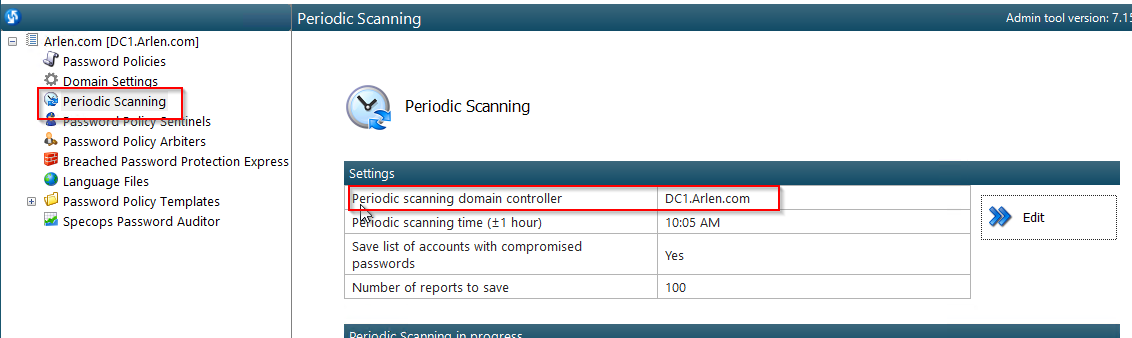
Then Validate within the “Periodic Scanning” Menu that the DC is reflective of the new PDC and if not click edit on the right hand side to change it to the correct DC: